
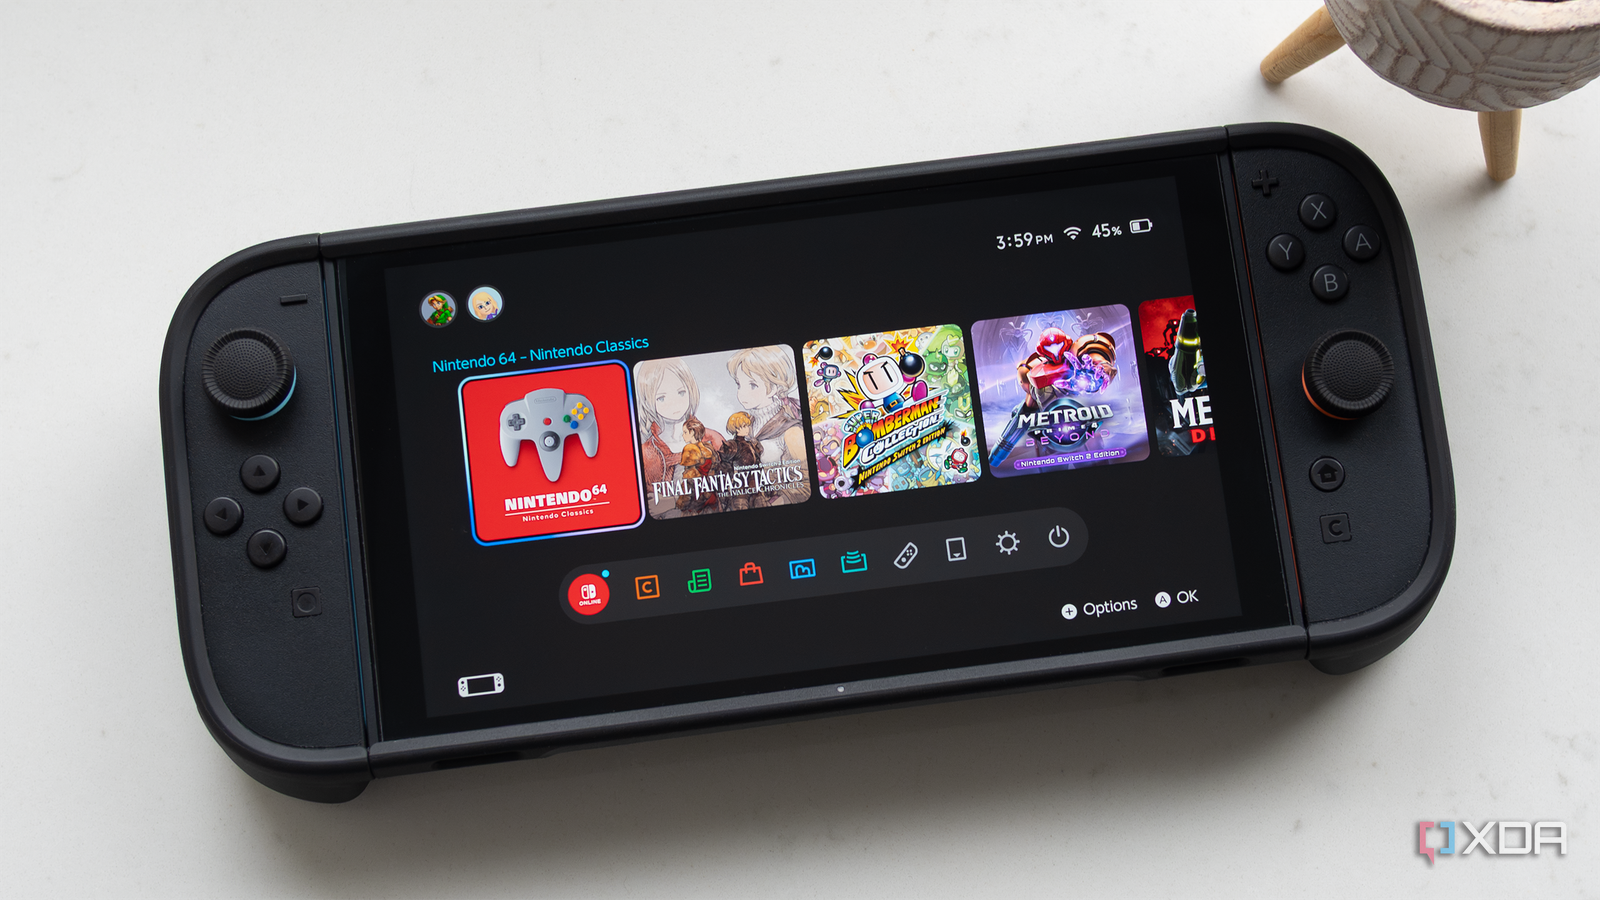
Published Oct 22, 2026, 9:52 AM EDT Patrick O'Rourke is XDA's News Editor and Entertainment Segment Lead. Previously, he was Pocket-lint's Editor-in-Chief, the Editor-in-Chief of Canadian tech publication MobileSyrup, and earlier in his career, he worked as the technology editor at the Financial Post and Postmedia. He's based in Toronto. Over the past 15 years, he's written thousands of articles. Patrick has also interviewed dozens of tech industry executives and covered GDC, E3, Gamescom, WWDC, Apple keynotes, Samsung Unpacked events and more. Patrick has a BA in journalism from Toronto Metropolitan University. Sign in to your XDA account Summary The Switch 2 has been jailbroken using OpenAI's Codex and SmileBASIC 4 on firmware version 23.0.1. The jailbreak's creator used the tethered exploit to add Peter Griffin, Hatsune Miku, and Cinnamoroll to Mario Kart World. Nintendo will likely pull the SmileBASIC 4 tool and push out a firmware patch. Following the recent release of a PlayStation 5 jailbreak, Nintendo's Switch 2 has officially been cracked open, thanks to a hefty dose of help from OpenAI's Codex coding agent. Twitter user Sammy Hajhamid (Pepsipu) recently posted that they "jailbroke" the Switch 2, allowing them to add Family Guy's Peter Griffin, Hatsune Miku, Sanrio's Cinnamoroll, and of course, an Angry Bird, to Mario Kart World — because, of course, that's the first thing anyone would do as soon as they've opened up a notoriously locked-down console. Their post also includes a video of the game in action, suggesting the exploit is legitimate. In a bold move given Nintendo's litigious history, Pepsipu goes so far as to outline exactly how they accomplished the jailbreak in a detailed blog post (I'm not linking to the exploit, but it's pretty easy to find). In the blog post, Pepsipu explains that the jailbreak was built with help from OpenAI's Codex and exploits SmileBASIC 4, a $25 eShop app that's a game-building tool. It also runs on the Switch 2's latest 23.0.1 firmware. "The very first thing I did was set up a harness around the Switch 1 and 2 so Codex could, ideally, jailbreak the Switch 2 without me," Pepsipu writes in the blog post. They add that the jailbreak still took "substantial effort" and that development lasted 2 weeks. Pepsipu also mentions that the Mario Kart World mods were vibe-coded in a day. "The JetKVMs allow Codex to send controller inputs to the Switches over USB and receive video output over HDMI. We also need a way to press the power button — when the Switch 2 crashes, it needs a button press to restart." To accomplish this, they used a physical "Bluetooth light switch flicker" from Amazon. Codex then used WebKit, an open-source browser engine, to run code through the handheld's browser and implement the exploit. It seems like Codex targeted SmileBASIC 4 because it's been used in other expoits in the past. The Switch 2 jailbreak is already publicly available This likely won't be around for long Over the next few hours, I wouldn't be surprised if Nintendo pulled SmileBASIC 4 from the eShop once steps to accomplish this jailbreak appear online. It's also very possible that Nintendo will quickly patch the exploit out with a hastily pulled-together Switch 2 firmware update. It's important to note that this is a tethered jailbreak, which means that whenever the console is shut down, you lose everything. On a side note, I don't think I've heard the term "tethered jailbreak" since the heyday of iPhone jailbreaking. Remember Redsn0w and the Cydia store? This Switch 2 jailbreak arrived just after the PS5 was cracked wide open, allowing it to run PS2 emulators with support for original discs.
The Nintendo Switch 2 has finally been jailbroken for the first time with a lot of help from AI
Full Article
Original Source
Read the full article at Xda-developers →KhanList aggregates and links to publicly available news content. We do not host full articles from third-party sources. Always verify important information with original sources.