
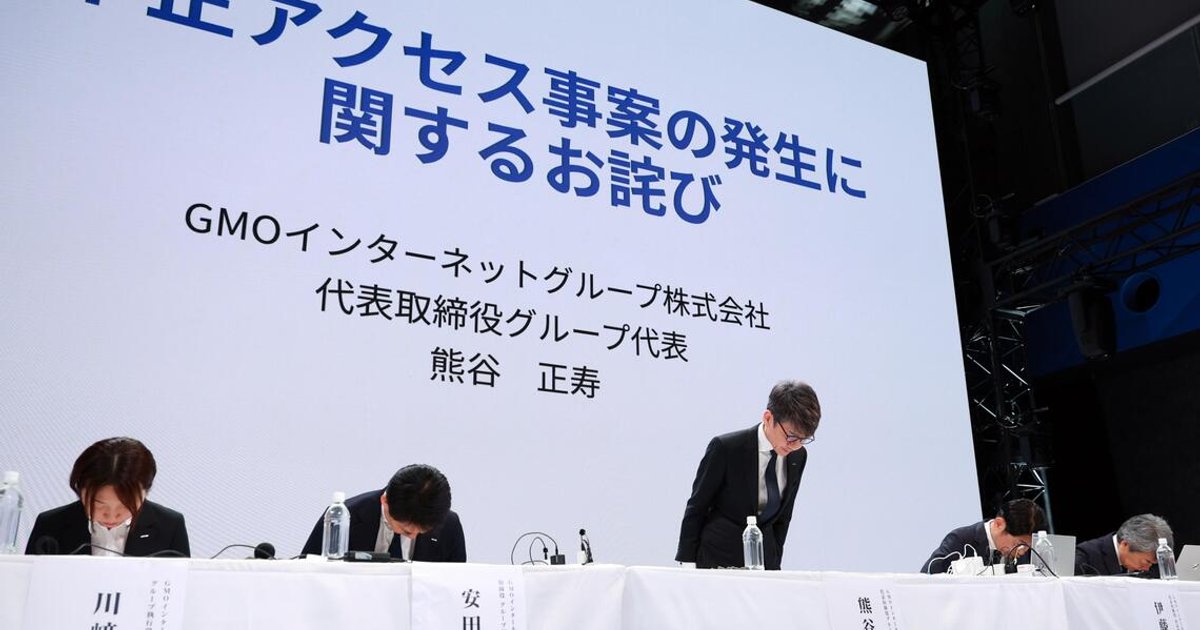
TOKYO – GMO Internet Group CEO Masatoshi Kumagai said on Nov 2 that the company had failed to adequately address a security vulnerability despite being alerted to the weakness in 2024, before a recent cyberattack resulted in a data leak.At the firm’s first press conference since the cyberattack surfaced in October, he apologised for the incident and for the damage to customers’ assets. The company announced that Kumagai and three other executives will be slapped with pay cuts.“We were not able to utilise (the vulnerability alert) in the operation of the service,” said Kumagai, who will take a 30% cut in his remuneration for three months.“We deeply apologise to our customers for not being able to protect them,” he added.Experts at a group company flagged the vulnerability in April 2024.The company had concluded that the problem was fixed through extraordinary maintenance work after it was brought to its attention, but an executive said at the press conference: “Our risk analysis was insufficient.”An attacker intruded the server on Aug 5, 2026. GMO was unaware of the attack until Oct 20, a day after a customer inquired about some suspected unauthorised transactions, and it confirmed that a third party had installed an unauthorised program in the server environments of some customers.The unauthorised access targeted the Onamae.com Desktop Cloud service, which is used for foreign exchange trading.The intrusion route and the full scope of financial damage inflicted by the unauthorised access are not yet known, according to the company.Sources close to the matter say GMO told the Japanese government that a North Korea-linked hacking group was likely behind the cyberattack. But the company did not elaborate on the matter at its press conference.The Tokyo police have launched an investigation involving some 70 investigators into a suspected violation of the law prohibiting unauthorised computer access, investigative sources said on Nov 2.GMO consulted the Metropolitan Police Department on Oct 22.The alleged attacker has not contacted GMO since the night of Oct 23, the company said.On Oct 27, a hacker believed to be behind the unauthorised intrusion disclosed some customer information after threatening to release it.In a statement, the hacker claimed that information linked to one GMO customer had been posted online after the company failed to respond to a US$1 million (S$1.28 million) ransom demand.The disclosed information included a name, address and other personal details, though its authenticity was unclear. KYODO NEWS
Cyberattack-hit GMO left system vulnerable for over 2 years, says CEO
Full Article
Original Source
Read the full article at Straitstimes →KhanList aggregates and links to publicly available news content. We do not host full articles from third-party sources. Always verify important information with original sources.